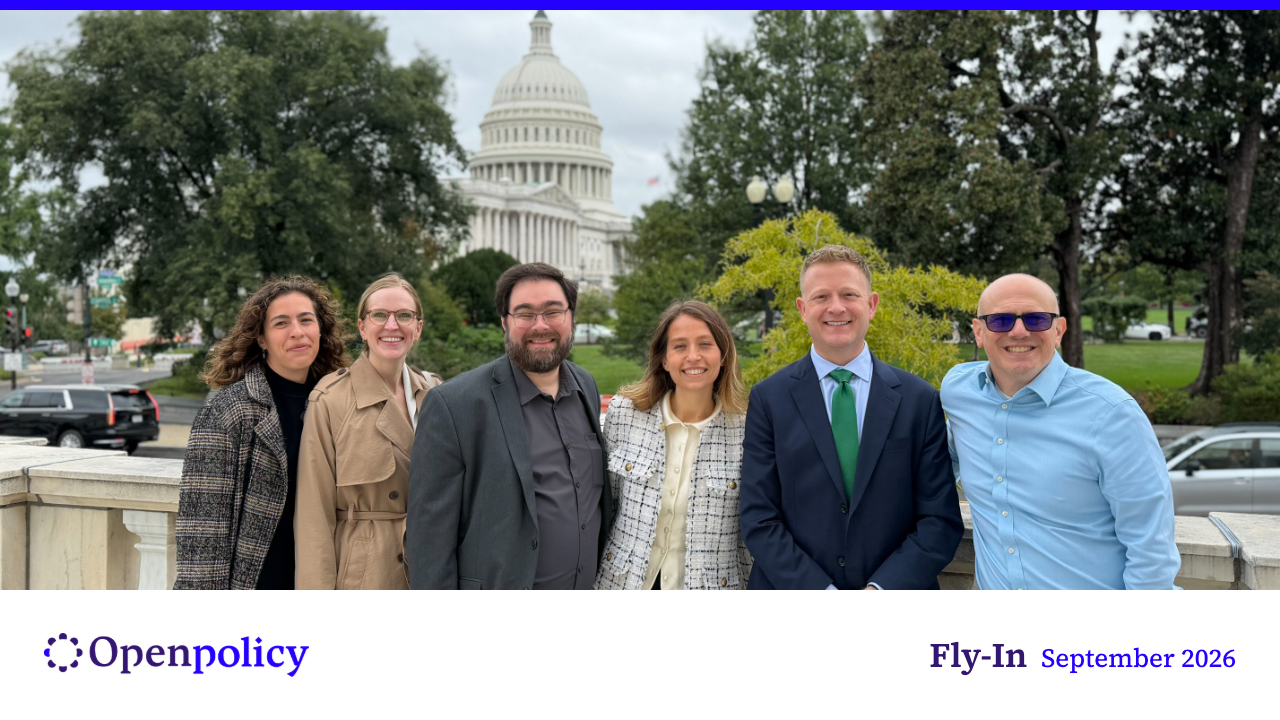
OpenPolicy’s Coalition Fly-In brings industry leaders and technical experts to Washington, D.C. for direct conversations with policymakers on the technology and security issues shaping the policy agenda. The September Fly-In focused on AI security, creating an opportunity to share real-world industry perspectives and discuss where policy can most effectively support a rapidly evolving technology landscape.
After two days of conversations with congressional offices, one thing was clear: policymakers want a better understanding of how AI security is being implemented in practice, which industry standards and best practices already exist, where the real gaps remain, and where federal policy can add value.
Three key takeaways the coalition learned from the fly-in:
1. Federal policy should look to industry best practices and remain adaptable as technology evolves: Policymakers are still assessing which existing standards and security practices already address emerging risks, where genuine gaps remain, and how policy can address those gaps without locking in requirements that may quickly become outdated.
2. AI security is a full-stack cybersecurity challenge, not just a model-security issue: The conversations repeatedly came back to the broader technology environment—hardware, infrastructure, software, data, identity, models, and agents. Securing that environment requires visibility across layers, continuous monitoring, and the ability to respond when something changes, while drawing on established cybersecurity and zero-trust principles.
3. Industry expertise is increasingly important to effective technology policy: As technologies, architectures, and security risks evolve, policy questions are becoming more complex. Real-world technical and operational experience can help translate those changes into practical, informed policy approaches.
The conversations reinforced how important it is for policy to stay connected to how security is actually being implemented in practice and how valuable continued collaboration between policymakers, industry, and technical experts will be as technologies and risks evolve.
Thank you to our coalition members and to the congressional offices that engaged with us in Washington, D.C. We look forward to continuing that collaboration.
Amanda Goff, Bob Joachim, Taylor Roberts, John Loucaides, Jason Silbergleit